An intent-service compliance program is a documented operating system for data inventory, lawful and permitted use, contracts, notices, rights handling, security, retention, subprocessors, client separation, activation, incidents, training, and audits. A badge or policy page is not enough. Requirements vary by jurisdiction, industry, data type, contract, and channel, so qualified counsel must review the real implementation.
Who this is for: Agency owners, operations leaders, privacy and security owners, RevOps firms, and resellers governing intent, identity, enrichment, visitor, and activation workflows across clients.
Intent data should improve a decision. It should never be presented as proof that a person is ready to buy or as permission for an unreviewed action.
BrandWell update, September 2026: MarketPulse intent data starts at $250/month within BrandWell’s complete growth automation software. AIMEE, the agent-powered desktop app, helps connect buyer signals with research, content, and campaign work. Access to the broader tools depends on your package.
Decide whether an agency intent-service compliance program fits the client
Decide whether the agency can explain every material data flow, purpose, user, client, field, decision, recipient, retention period, and deletion path. Promise documented controls and review, not universal legal compliance or certification. Keep legal conclusions with qualified counsel.
A seven-step agency intent-service compliance program workflow
- 1. Inventory clients, systems, sources, fields, purposes, identity states, recipients, regions, and retention.
- 2. Map contracts, roles, permitted use, resale, end-client access, subprocessors, and data rights.
- 3. Apply purpose limitation, minimization, least privilege, tenant separation, suppressions, and secure transfer.
- 4. Create notice, correction, opt-out, deletion, export, complaint, and escalation workflows.
- 5. Review every CRM write, audience upload, outreach route, model use, and automated decision boundary.
- 6. Train staff, test controls, record incidents, and complete periodic access and vendor reviews.
- 7. Update the program when laws, contracts, sources, purposes, channels, or systems change.
Build the evidence log for an agency intent-service compliance program
Use one versioned record to show why each agency intent-service compliance program decision was made. Capture the eligible market, topic definition, source, observed time, identity state, validation result, suppression, reviewer, approved action, downstream disposition, and fully loaded cost. Preserve rejected, expired, duplicated, and corrected records with reason codes rather than overwriting them. This makes client explanations and later comparisons reproducible.
Open the log with Inventory clients, systems, sources, fields, purposes, identity states, recipients, regions, and retention. Close each review cycle with Update the program when laws, contracts, sources, purposes, channels, or systems change. If a topic, source, identity rule, activation path, outcome definition, price, or policy changes, record the approver, affected records, and whether prior periods remain comparable.
Five control domains in an agency intent-service compliance program
1. Data inventory and purpose
Record sources, fields, identities, clients, purposes, recipients, regions, and retention.
Watch-out: Unknown data cannot be governed reliably.
2. Contracts and vendor oversight
Review licensing, resale, end-client use, roles, subprocessors, security, incidents, rights, and exit.
Watch-out: Marketing descriptions do not establish legal permission.
3. Access and tenant separation
Use least privilege, role reviews, logging, strong authentication, and client isolation.
Watch-out: Convenient shared access can create severe cross-client risk.
4. Activation and communication controls
Review CRM writes, audience uploads, outreach, personalization, suppression, and human approvals.
Watch-out: Possessing data does not make every use appropriate or permitted.
5. Rights, incidents, and assurance
Operate correction, opt-out, deletion, export, complaint, incident, training, testing, and audit workflows.
Watch-out: A policy without tested operations provides weak assurance.
Copy this agency intent-service compliance program decision worksheet
Use this field set during discovery, onboarding, and the first client review. It turns an agency intent-service compliance program into a reproducible decision record instead of an informal promise. Replace every bracketed prompt with written evidence and leave unknowns visible.
AGENCY INTENT-SERVICE COMPLIANCE PROGRAM DECISION WORKSHEET
Client decision: [one decision this service must improve]
Eligible market and exclusions: [written ICP, geography, lifecycle, customers, competitors]
Evidence required: [source, observed time, topic rule, identity state, validation]
Path being evaluated: [Data inventory and purpose; Contracts and vendor oversight; Access and tenant separation; Activation and communication controls; Rights, incidents, and assurance]
First operating control: [Inventory clients, systems, sources, fields, purposes, identity states, recipients, regions, and retention.]
Final operating control: [Update the program when laws, contracts, sources, purposes, channels, or systems change.]
Owners and approvals: [agency, client, data, CRM, activation, privacy, billing]
Fully loaded monthly cost: [platform + usage + labor + support + risk reserve]
Evidence of use: [accepted, rejected, corrected, acted on, downstream disposition]
Stop, revise, or expand rule: [threshold, reviewer, next action]
Package an agency intent-service compliance program as a recurring client operation
Translate the workflow into a client scope for an agency intent-service compliance program: the decision being improved, eligible market, topic set, branded deliverable, portal or export, action SLA, review cadence, usage boundary, support path, change control, and stop rule. Mark records as eligible, review, suppressed, expired, or unresolved so the client knows what can happen next.
Assign named owners for sales, client success, data operations, identity review, CRM, activation, privacy, security, analytics, and billing. Attach evidence to every handoff. Review the first month as an operating test by comparing accepted, rejected, corrected, suppressed, and acted-on records with delivery hours, outcome return, and contribution margin. Narrow or stop the service when the client cannot use the evidence reliably.
BrandWell: MarketPulse intent data and connected growth automation
From audience to action: connect intent data with the work needed to use it. BrandWell is complete growth automation software that connects MarketPulse intent data, TrafficID website visitor identification, content, outreach, and campaign workflows. AIMEE, its agent-powered desktop app, helps turn those signals into research, prepared assets, and approved actions.
For this evaluation, review the audience, connected accounts, workflow owner, and approval settings together. The current app exposes ICP controls, team access, workflow approvals, and run history so the operating process can be examined alongside the data.
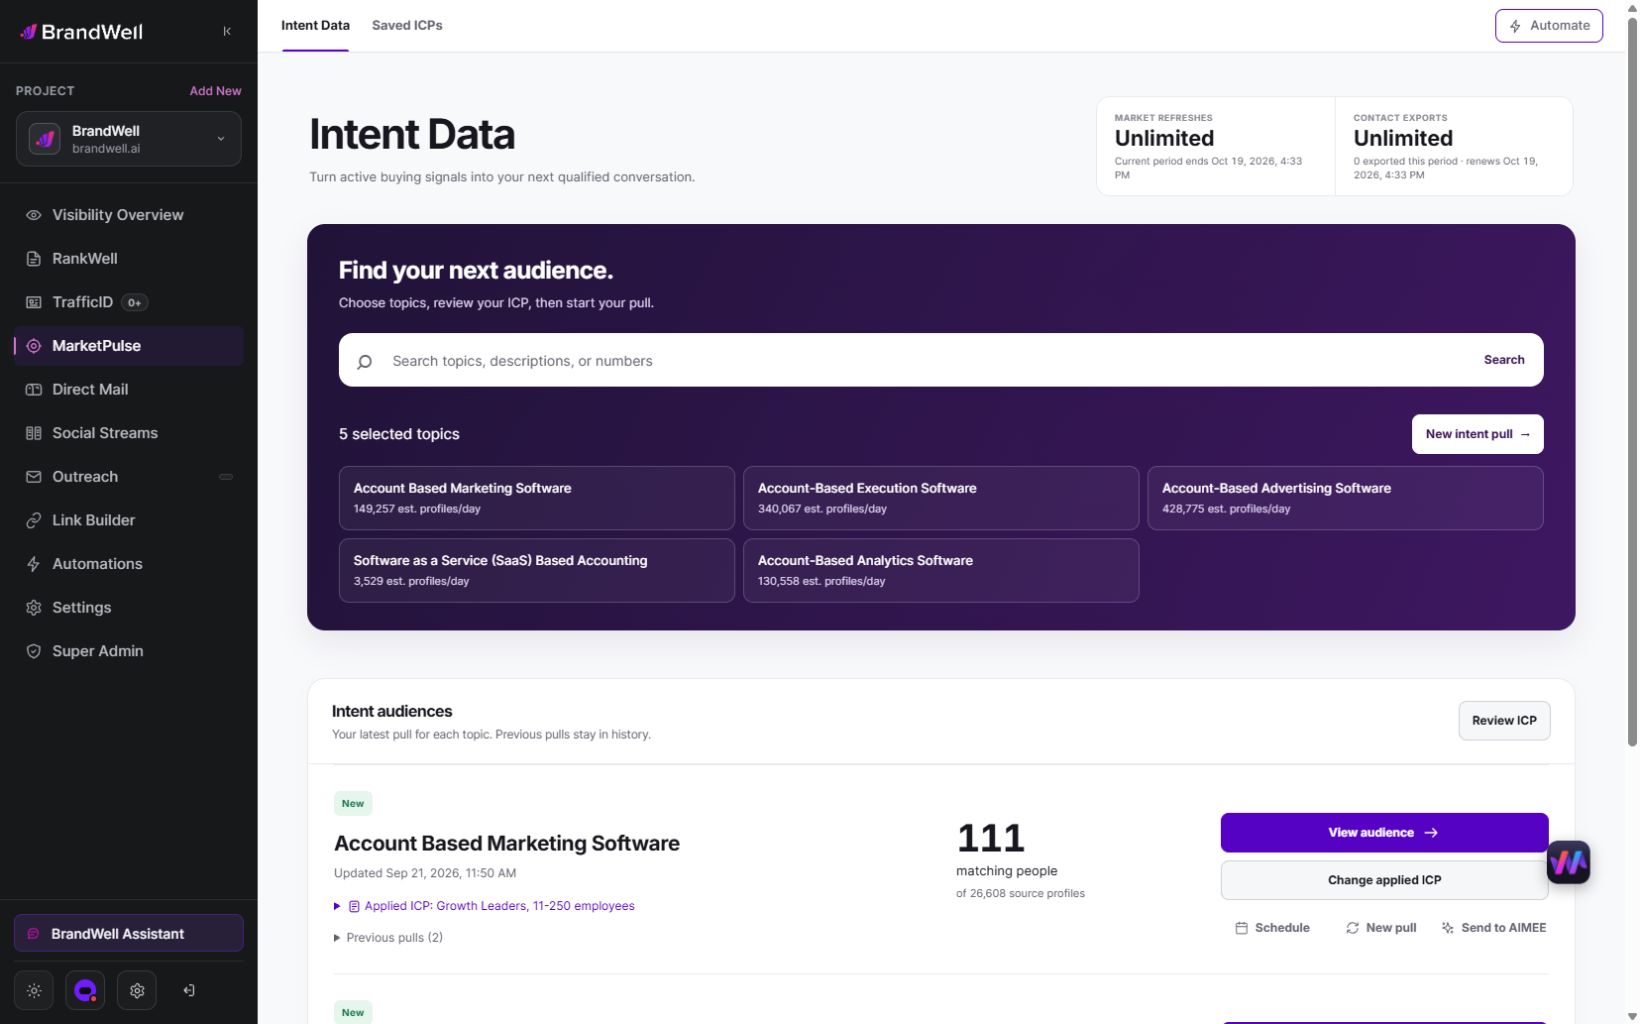
How the software connects the work:
- Find and qualify demand: MarketPulse brings topic-based intent into a reviewable audience with saved ICPs and scheduled pulls. TrafficID adds website visitor identification to the growth workflow.
- Prepare the next campaign: Outreach and Direct Mail provide execution workspaces; Social Streams adds relevant social activity. Use the tools and destinations configured for your project.
- Build demand as well as capture it: RankWell, Visibility Overview, and Link Builder connect content and visibility work with the same growth operation.
AIMEE helps carry the work forward
AIMEE is BrandWell’s agent-powered desktop app. It helps research accounts, prepare content and messages, and carry out assigned work through connected tools. BrandWell’s Automations workspace connects product events to workflow steps, with owners, approvals, and run history. You choose the connections, allowed actions, and budgets.
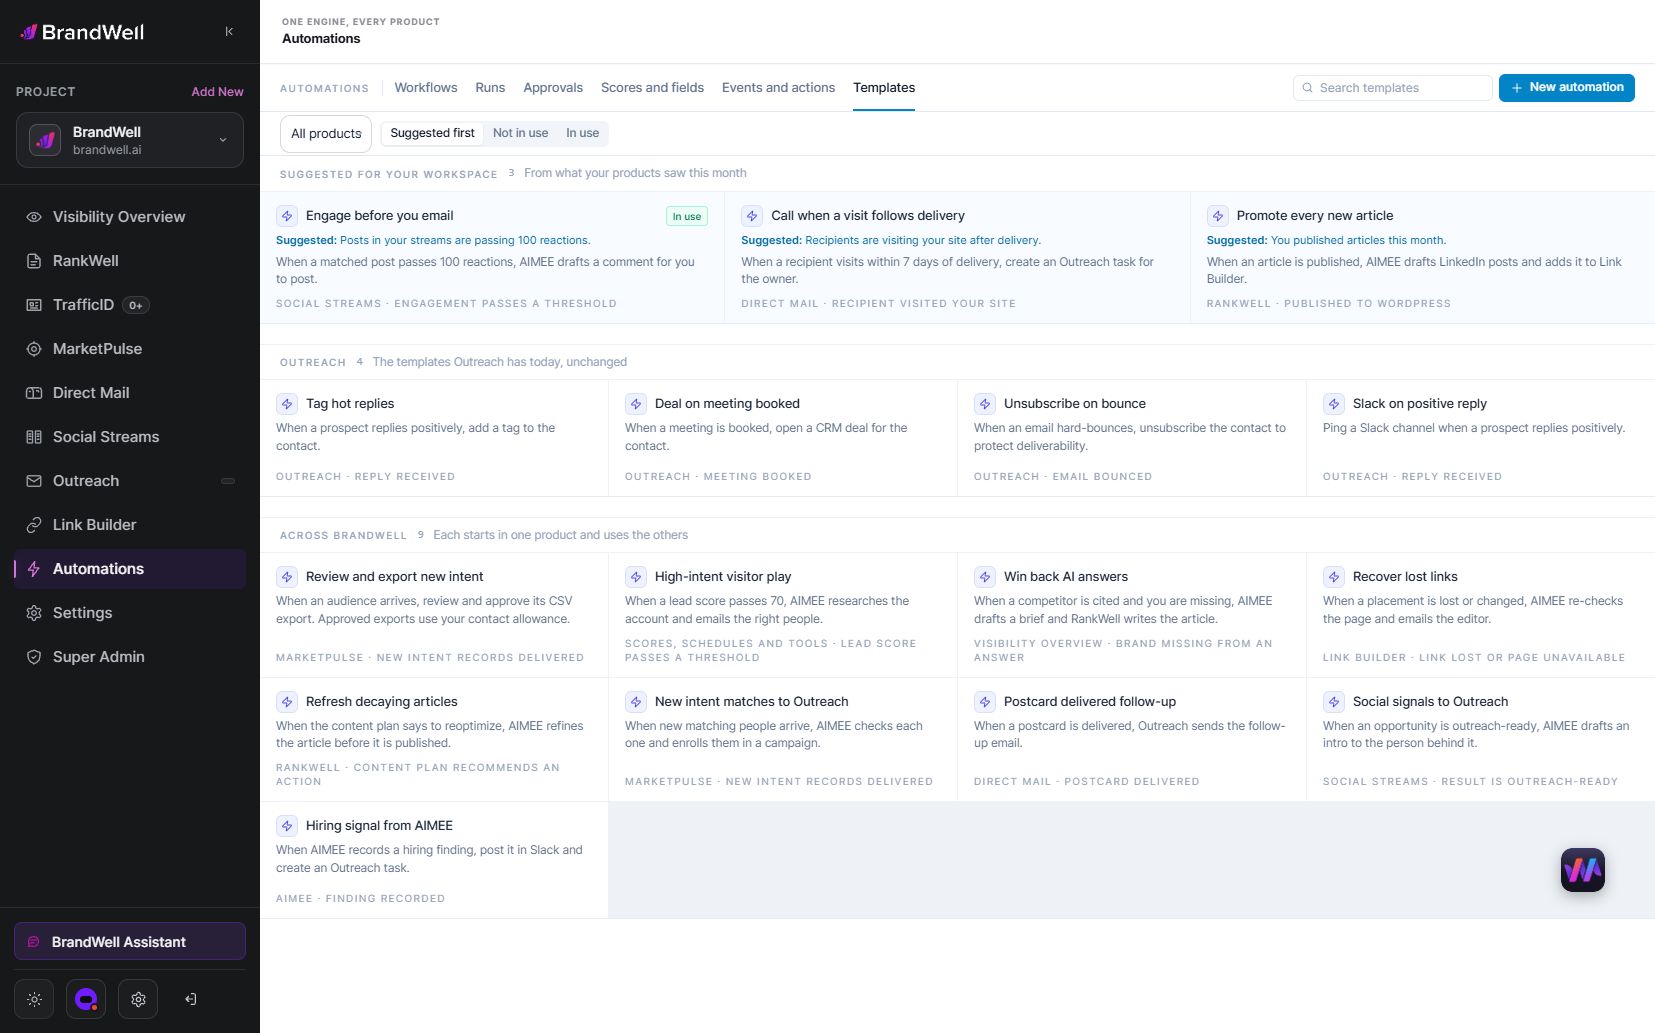
BrandWell MarketPulse intent-data plans start at $250/month. Your selected package determines topic coverage, contact allowances, refresh cadence, AIMEE access, and other growth tools. Channel usage, media, and fulfillment costs depend on the campaign.
What to evaluate: topic relevance, usable audience coverage, ICP fit, and the time it takes to turn an accepted signal into completed work. An intent signal helps prioritize an opportunity; it does not guarantee a purchase or establish permission for every channel. Choose a workflow your team can operate, then evaluate the audience and the completed work against that goal.
How BrandWell fits into an agency intent-service compliance program
Here, BrandWell means the current MarketPulse intent-data and growth automation platform, connected with the broader BrandWell content and growth tools. LeadFuze supplies underlying data capabilities where contracted and available. BrandWell is designed as a complete growth automation platform with agency delivery options with branded topic reports, portal and client workflows, modular services, configurable retail pricing, and controlled activation. The exact modules, coverage, usage, support, client capacity, and implementation in the current written quote control.
Start with MarketPulse intent data from $250/month. Review a topic and its matching audience, then use BrandWell’s connected growth tools and AIMEE desktop assistance to prepare the next action. Agency packaging and services can be scoped around the client workflow.
BrandWell MarketPulse intent-data plans start at $250/month. Your selected package determines topic coverage, contact allowances, refresh cadence, AIMEE access, and other growth tools. Channel usage, media, and fulfillment costs depend on the campaign. Compare total cost for the same audience, tools, implementation, and campaign scope; starting prices alone do not establish the lowest-cost provider.
AIMEE is the agent-powered desktop app in BrandWell’s growth workflow. Assign work through the tools connected to your workspace and choose which actions can run automatically or require approval. Desktop availability, account permissions, and the configured workflow determine what can execute.
Price and measure an agency intent-service compliance program
Budget counsel, privacy and security leadership, vendor due diligence, contracts, inventory, technical controls, rights handling, training, testing, insurance, incidents, and audits. Compliance is a continuing operating cost. Price the service so required controls are funded rather than treated as optional overhead.
The agency intent-service compliance program stop-or-expand scorecard
Track inventory coverage, vendor reviews, access reviews, training, rights-request completion, suppression propagation, retention deletion, incident detection and response, client exceptions, control tests, remediation time, and audit findings. Metrics show operations, not a guarantee of legal compliance.
Important: Intent signals are probabilistic evidence. They do not prove identity, consent, need, authority, budget, stage, qualification, purchase, pipeline, or revenue. Report association and uncertainty honestly.
Guardrails for an agency intent-service compliance program
Risks include making legal claims without counsel, using personal or sensitive data beyond purpose, weak notices, invalid resale, cross-client exposure, missing subprocessors, insecure transfers, unreviewed automated actions, and failure to honor rights or deletion. Escalate uncertainty instead of inventing permission.
The FTC business security guidance recommends collecting only what is needed, limiting access, and disposing of information no longer required. The NIST Privacy Framework offers a voluntary structure for identifying and managing privacy risk. These resources are not legal advice or certifications. Obtain qualified counsel for the actual jurisdictions, contracts, data flows, industries, and channels.
- Preserve source, observed time, identity state, confidence, validation, and policy version.
- Separate known people, candidate people, companies, domains, and unresolved visitors.
- Apply customer, employee, competitor, duplicate, geography, consent, and opt-out suppressions.
- Require named human approval before CRM writes, audience uploads, spend, or outreach.
- Give clients correction, export, deletion, escalation, incident, and offboarding paths.
Run the agency intent-service compliance program review with Claude, ChatGPT, or AIMEE
Objective: Audit an intent-service control register using approved inventory, contracts, client roles, source permissions, identity states, users, systems, subprocessors, regions, retention, rights, suppressions, activations, incidents, training, and tests. Return gaps and owners. Do not issue legal conclusions or certifications.
Inputs: approved ICP, topic dictionary, signal source and time, identity state, client lifecycle, suppressions, permitted-use policy, outcome definitions, and current written commercial scope.
Rules: preserve provenance and uncertainty; never infer budget, authority, consent, or purchase readiness; never expose private behavior in messaging; stop before external action.
Output: decision, reason codes, missing evidence, recommended next step, and audit log.
The NIST AI Risk Management Framework is a useful voluntary reference for roles, oversight, measurement, third-party risk, and ongoing management. It does not validate a specific workflow or remove the need for human review.
Method and maintenance for an agency intent-service compliance program
This guide evaluates an agency intent-service compliance program through one defined client decision, a seven-step operating workflow, consistent option criteria, a fully loaded cost model, an outcome scorecard, and explicit limitations. The featured image is decorative and is not evidence of product performance or a client outcome. Current contracts, official product documentation, platform policies, and scope-matched written quotes control volatile facts.
Recheck the relevant claim before a client quote and whenever a provider changes pricing, modules, permitted uses, reseller rights, retention, export, support, platform policy, or contract terms. Revise the affected statement and workflow rather than carrying an old assumption into a new engagement.
Related agency intent-service guides
Use these companion guides to move from the current decision into the next operating layer without collapsing distinct buyer questions into one oversized page.
- Intent-Data Client Onboarding Checklist for Agencies
- Intent-Data Reporting for Agencies: Metrics, Templates, and Workflows
- How to Choose an Intent-Data Vendor for an Agency Service
Direct answers to ten buyer questions about intent service compliance program
What should an agency decide before building an intent-data compliance program for an agency, and what client outcome can it responsibly promise?
Make a go, revise, or stop decision before delivery begins. The governing test is: Decide whether the agency can explain every material data flow, purpose, user, client, field, decision, recipient, retention period, and deletion path. Promise documented controls and review, not universal legal compliance or certification. Keep legal conclusions with qualified counsel.
What workflow, owners, SLA, quality checks, approvals, and client handoff does an agency intent-service compliance program require?
Assign a named agency owner, client owner, operator, and technical or CRM owner. The sequence is: 1) Inventory clients, systems, sources, fields, purposes, identity states, recipients, regions, and retention. 2) Map contracts, roles, permitted use, resale, end-client access, subprocessors, and data rights. 3) Apply purpose limitation, minimization, least privilege, tenant separation, suppressions, and secure transfer. 4) Create notice, correction, opt-out, deletion, export, complaint, and escalation workflows. 5) Review every CRM write, audience upload, outreach route, model use, and automated decision boundary. 6) Train staff, test controls, record incidents, and complete periodic access and vendor reviews. 7) Update the program when laws, contracts, sources, purposes, channels, or systems change. Set the response SLA, log exceptions, preserve uncertainty, and require a client handoff with permitted next steps and ownership.
Which platforms, tools, templates, calculators, and integrations best support building an intent-data compliance program for an agency?
Start with the operational resources in this guide: Data inventory and purpose, Contracts and vendor oversight, Access and tenant separation, Activation and communication controls, Rights, incidents, and assurance. Use the client CRM as the outcome system of record, a permissioned review queue or database for evidence, the copyable worksheet in this guide, a topic dictionary, qualification scorecard, cost calculator, responsibility matrix, client report, and approval checklist. Add integrations only after field IDs, permitted writes, owners, retries, deletion, and exception handling are documented for an agency intent-service compliance program.
How do centralized, client-specific, vendor-led, counsel-led, and framework-aligned compare for building an intent-data compliance program for an agency?
Compare centralized, client-specific, vendor-led, counsel-led, and framework-aligned against the same client decision, market, evidence, owners, SLA, implementation time, fully loaded cost, governance, outcome scorecard, and exit path. The right approach to building an intent-data compliance program for an agency is the one the client can adopt and the agency can deliver repeatedly without hiding labor, rights, uncertainty, or risk.
How should an agency price an agency intent-service compliance program, and which setup, usage, labor, support, and risk costs determine gross margin?
Build a client-level cost model before setting price. Budget counsel, privacy and security leadership, vendor due diligence, contracts, inventory, technical controls, rights handling, training, testing, insurance, incidents, and audits. Compliance is a continuing operating cost. Price the service so required controls are funded rather than treated as optional overhead. Put usage overages, client work, exception handling, and out-of-scope activation in writing.
Which quality, adoption, meeting, opportunity, pipeline, cost, margin, and retention metrics show whether an agency intent-service compliance program is working?
Use a baseline and one review cadence. Track inventory coverage, vendor reviews, access reviews, training, rights-request completion, suppression propagation, retention deletion, incident detection and response, client exceptions, control tests, remediation time, and audit findings. Metrics show operations, not a guarantee of legal compliance. Do not call correlation incremental impact without an appropriate comparison.
Which clients are ready for an agency intent-service compliance program, and which prospects should the agency exclude?
A client is ready for an agency intent-service compliance program when it has a clear ICP, sufficient market or qualified traffic, relevant commercial topics, a named action owner, measurable outcomes, conservative economics, privacy readiness, and a way to return dispositions. Require this first control: Inventory clients, systems, sources, fields, purposes, identity states, recipients, regions, and retention. Exclude clients demanding guaranteed leads, universal identity, prohibited use, or automation without review.
Which signal sources, identity checks, qualification rules, activation steps, and outcome evidence matter most for an agency intent-service compliance program?
For an agency intent-service compliance program, combine topic or first-party behavior with fit, recency, recurrence, identity state, validation, suppressions, human acceptance, the approved activation path, and returned outcomes. Apply the specific controls in this workflow: Map contracts, roles, permitted use, resale, end-client access, subprocessors, and data rights. Apply purpose limitation, minimization, least privilege, tenant separation, suppressions, and secure transfer. Keep evidence types separate so an inference never becomes a false fact.
Which data-quality, privacy, security, scope, billing, delivery, and client-trust risks must the agency control for an agency intent-service compliance program?
Maintain a risk register owned by the agency and client. Risks include making legal claims without counsel, using personal or sensitive data beyond purpose, weak notices, invalid resale, cross-client exposure, missing subprocessors, insecure transfers, unreviewed automated actions, and failure to honor rights or deletion. Escalate uncertainty instead of inventing permission. Record the control, owner, evidence, exception path, and next review for every material risk.
What should the compliance register, evidence file, review cadence, and escalation path include?
Treat the answer to this question as the acceptance test: What should the compliance register, evidence file, review cadence, and escalation path include? Connect the decision to five control domains in an agency intent-service compliance program. Document scope, owners, evidence, delivery cadence, approvals, usage, price, scorecard, support, change control, and offboarding. Expand only after the client uses the initial scope and returns actionable dispositions.
The practical next step
Start with MarketPulse intent data from $250/month. Review a topic and its matching audience, then use BrandWell’s connected growth tools and AIMEE desktop assistance to prepare the next action. Agency packaging and services can be scoped around the client workflow.